
Loading...

What is GDPR?
How ISO:27001 And GDPR Related With Each Other?
- Data Integrity, Availability, Confidentiality
- Risk Assessment
- Notification Of Data Breaches
- Data Protection Measures
- Documenting Security Processes
How SPEC INDIA is GDPR-Compliant?
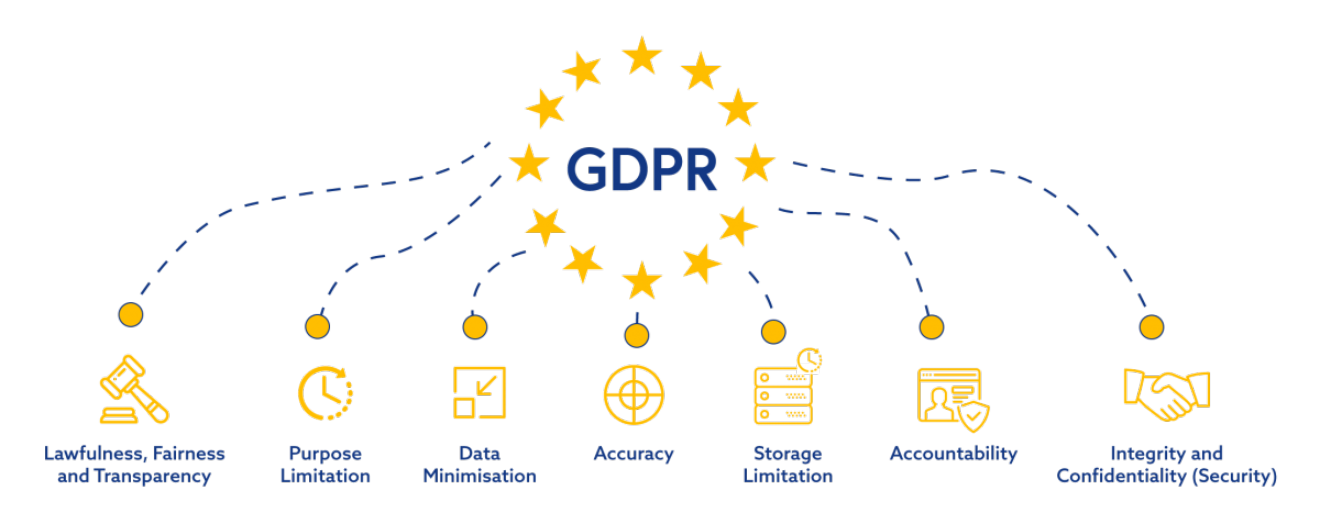 With globally-present clientele, and especially in the European region, we have taken several considerations into account to safeguard data at every level.
GDPR Practices We Follow To Ensure GDPR-Readiness
- Deletion/Modification Of DataAccording to GDPR standards, EU citizens have rights to ask for data erasure and modification of data
- Secure Communication ChannelsWe use secure communication channels to ensure complete security and privacy of communication
- Data Protection OfficerWe have appointed DPO ( Data Protection Officer) who oversees data protection strategy and ensures compliance with GDPR
- Consent of UsersWe obtain the consent of users to support EU User consent policy for the use of cookies and any other data collection
- Encrypted DataOur system stores encrypted data and manage end-to-end security controls while processing
- Notification of BreachesWe ensure, when a data breach occurs, we report that within 72 hours.
SPEC INDIA’s Security-First Approach For ISO And GDPR Compliance
- We have already initiated a drive to achieve ISO 27001 standard in 2nd quarter of 2019. We expect to get the certificate in the 4th quarter of 2019, ensuring complete security under control.
- Our QMS team maintains a healthy security structure enabling compliance with international data regulations
- To comply with GDPR regulations at every level, we have conducted internal sessions on GDPR.
- We constantly look forward to adopting the best security practices that are in line with GDPR compliance. Our teams are well aware of the importance of data security in the data-driven age, adopting best practice to strengthen data security controls and mitigate risks.
Let’s get in touch!
India
SPEC House, Parth Complex, Near Swastik Cross Roads, Navarangpura, Ahmedabad 380009, INDIA.
-
 +91-79-26404031, 32-33-34
-
 [email protected]